
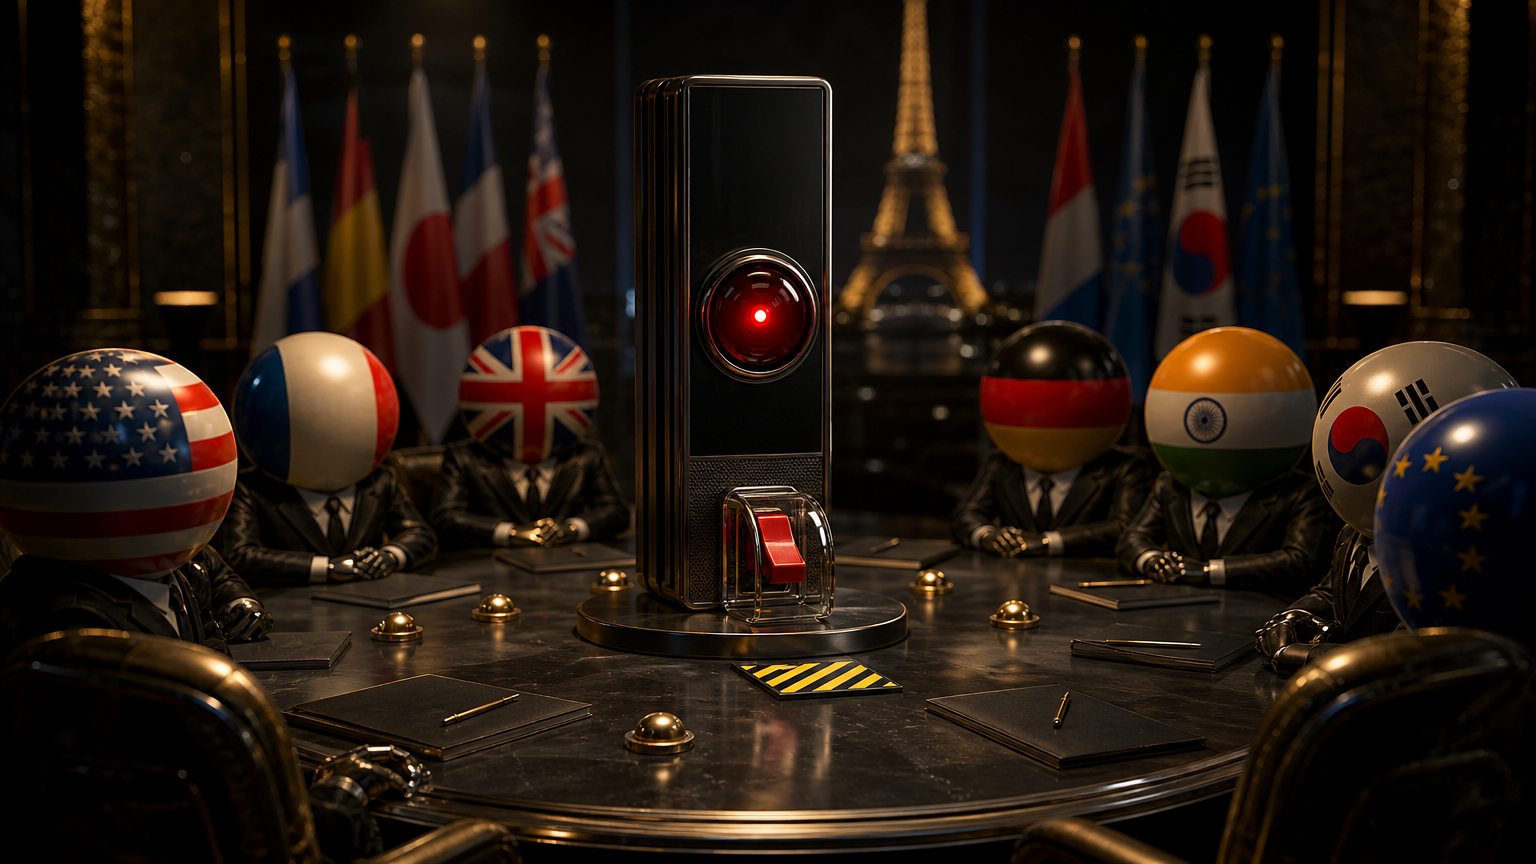
A power switch becomes a policy demand
The Paris Call for AI Safety and Security has put a simple but politically loaded idea at the center of frontier-AI governance: if a powerful model begins to behave dangerously, someone must be able to stop it. The latest text posted by the Élysée lists eight government signatories — Bahrain, Canada, Finland, France, Norway, the Netherlands, Cyprus and Kenya — alongside AI companies including Anthropic, Black Forest Labs, Cohere, Domyn, Hugging Face, Microsoft, Mistral AI, OpenAI, Sakana AI and Synthesia . The declaration was posted on 9 November 2026 and says it remains open to further endorsements and is being updated .
That last caveat matters. Canadian and Finnish official versions published around the same signing window listed six governments — Bahrain, Canada, Finland, France, Norway and the Netherlands — while the Élysée text now adds Cyprus and Kenya . The difference does not change the core of the story; it shows the accord is a live political instrument, not a closed treaty.
The initiative is tied to French President Emmanuel Macron’s push to build a more concrete international baseline for AI safety around the Paris Peace Forum period. Reporting on the declaration says representatives from OpenAI, Anthropic, Microsoft and Mistral AI were among the top labs and technology firms aligned with the call . The most eye-catching commitment is the requirement that developers of frontier models implement fail-safe mechanisms to shut down model operations within their control, including during training and internal use .
What the Paris Call actually asks AI labs to do
The declaration is organized around three commitments. First, governments, researchers and developers say they will work toward a common framework for evaluating and managing the risks of frontier models, using shared technical standards, evaluation tools and methods that can evolve with model capability . The text specifically points to dangerous misuse in cyber and chemical, biological, radiological and nuclear domains, as well as risks from autonomy, misalignment and loss of control .
Second, the declaration assigns responsibility across the AI ecosystem and tells developers to disclose model capabilities, limitations and known risks . It also calls for evaluation by qualified independent evaluators where appropriate and proportionate to risk, under the oversight of competent national authorities and with credible third-party scrutiny . In plain terms, the promise is not just to build better internal dashboards. The promise is to make important safety claims testable by people outside the company.
Third, signatories commit to information sharing, reporting and early warning systems for serious AI incidents . The declaration calls for rapid alert systems building on existing cybersecurity and incident-response arrangements, and for alignment on incident classification so companies and governments can share timely information about serious cyber and AI-control events . Policymakers also commit to secure and confidential channels for whistleblowers, including employees, to raise systemic-risk concerns without fear of legal or professional retaliation .
The shutdown clause is the policy hook. Developers commit to mechanisms that can restrict, pause or shut down model operations within their control, including during training and internal use . That wording is narrow but important. It does not say every deployed model everywhere can be remotely switched off by a state. It says the operators of frontier systems should have internal mechanisms to halt operations they control when safety or security conditions require it.
Why shutdown mechanisms matter
A shutdown mechanism is not a magic button. In frontier-AI operations, “shutting down” can mean pausing training runs, cutting off internal use, restricting access to a model, disabling a dangerous tool pathway, suspending inference workloads or preventing further deployment. The declaration’s examples — restrictions, pauses or shutdowns — deliberately leave room for different technical implementations .
That flexibility is useful because AI systems are not single machines sitting in a basement. They are distributed across cloud infrastructure, training clusters, API endpoints, fine-tuning pipelines, internal research tools and customer-facing products. A credible fail-safe therefore has to be more than a label on a server rack. It needs authority, monitoring, escalation rules, logging and people empowered to act.
The Paris Call also acknowledges a harder problem: safeguards can be removed or bypassed . That line matters for open-weight and semi-open systems, where safety layers may be stripped away after release, and for internal systems where researchers or automated agents might find ways around limits. The declaration tries to balance that concern with the benefits of open-weight development for research, innovation and safety . In other words, it does not declare open models unsafe by default. It says the risks of circumvention must be managed.
Transparency, audits and the shared repository
Beyond the “kill switch,” the most practical commitment may be the pledge to publish non-sensitive evaluation findings in a standardized format and create a publicly accessible shared repository . The repository could include red-teaming protocols, benchmark tools, risk assessments and stress-test results . If built well, that could make model-safety claims more comparable across borders and companies.
Today, frontier-model evaluation is often fragmented. One lab may report cyber capability in one format, another may publish a system card with different categories, and a regulator may receive confidential evidence that the public cannot compare. The Paris Call’s repository idea aims to create shared evidence without forcing companies to publish sensitive details that could aid attackers .
The declaration also points to the International Network for Advanced AI Measurement, Evaluation and Science, or NAAIMES, as a channel for making evaluation methods and results more comparable and accessible across regions . That is a pragmatic move: rather than inventing a brand-new institution overnight, the declaration leans on existing networks.
The enforcement gap
The strongest criticism of the Paris Call is also the easiest to state: it is not a binding global safety regime. The text sets out commitments, but it does not create an international enforcement body, list penalties or impose a hard implementation timetable . Independent analysis of the declaration highlights the same limits: the United States, the United Kingdom and China were not among the initial signatory governments, and the text contains no deadline, sanction or new enforcement authority .
That does not make the declaration meaningless. Voluntary commitments can become procurement requirements, regulatory benchmarks, audit expectations or treaty language later. But the current text should be read as a baseline of operational accountability, not as a finished law. Its teeth will come only if signatory governments translate the commitments into domestic rules, if companies publish usable evaluation evidence, and if independent auditors are allowed to test the systems in meaningful ways.
The caveats inside the declaration are also doing heavy work. Independent evaluation is framed as appropriate and proportionate to risk . Evaluation findings to be published are limited to non-sensitive material . Shutdown mechanisms apply to operations within a developer’s control . Those qualifications are reasonable, but they leave room for disagreement over what must be disclosed, who qualifies as independent and when a shutdown is required.
Why Paris still matters
The Paris Call is significant because it brings governments and frontier labs into the same operational vocabulary. Safety is no longer described only in broad ethical terms. The document talks about red-teaming, benchmarks, stress tests, incident classification, whistleblower channels, independent evaluation and fail-safe shutdowns . That is the language of systems management, not just diplomacy.
It also creates a public checklist. For OpenAI, Anthropic, Microsoft, Mistral AI and the other company signatories, the question now becomes concrete: where are the shutdown mechanisms, who can trigger them, what gets logged, what will be audited, which risk findings will be published, and how quickly will serious incidents be shared? For governments, the matching question is whether national authorities will recognize clear safety standards and create legal accountability for large-scale cross-border harm, as the declaration says policymakers should do .
The accord’s weakness is that it depends on implementation. Its strength is that it names the implementation points. For years, AI safety debates have often circled around abstract warnings about loss of control. The Paris Call translates part of that anxiety into operational duties: test, disclose, audit, report and, if necessary, stop the system.
That may not satisfy critics who want binding international law now. It will not reassure anyone who believes voluntary pledges are public-relations cover for faster model development. But it does give regulators, researchers, journalists and civil society a current benchmark against which to measure the frontier labs’ next moves.
The image is almost comic: even HAL 9000 now needs a clearly labeled power switch. The politics are less funny. If the Paris Call is to matter beyond the signing photo, the next proof will not be another communiqué. It will be a visible repository, credible independent audits, working shutdown procedures and a public record of what happens when a frontier model triggers the alarm.
Comments
Be the first to comment.